
Deterministic Autonomous
Orchestration Engine
Unifying Autonomous AI Agents, Durable Workflows, Context Engineering, and Mission-Critical Connectivity into the ultra-efficient vFlow Rust core capable of running on 1 vCPU. Deployed 100% in your own private cloud or VPS (Onidel, Servury, VPSBG, Akash, Scaleway, AWS, GCP, Azure, Bare-Metal) with silicon TEE hardware protection from VastarIPShield and transparent per-vCPU pricing starting at $3 / vCPU.
Confidential VPS / Bare Metal / Cloud
In-Runtime Engine (Zero DMN Latency)
VWFD + VWFE + vFlow
AMD SEV-SNP / TDX / Nitro
schema: vastarorch.workflow/v1
kind: VastarOrchWorkflow
metadata:
  workflow_id: 11000000-0000-0000-0000-000000000005
  tenant_id: "00000000-0000-0000-0000-000000001000"
  workspace_id: "00000000-0000-0000-0000-000000002000"
  canonical_code: enterprise_operations_triage
  version: 1
  revision: 1
  name: "Autonomous Enterprise Operations Pipeline"
  description: "Enterprise multi-agent triage with deterministic guardrails, MCP tools, and human-in-the-loop approval."

interface:
  inputs:
    - name: incident_alert
      type: object
      required: true
  outputs:
    - name: triage_receipt
      type: object

activities:
  # 1. Ingress Webhook Trigger
  - id: incident_trigger
    activity_type: ao.activity.ingress.webhook
    contract_version: 1
    resources: []
    config:
      route: /api/v1/telemetry/incident-alert
      method: POST
      verification_mode: HMAC-SHA256

  # 2. Governed AI Agent Reasoning & Diagnostics
  - id: agent_triage
    activity_type: ao.activity.ai.agent.invoke
    contract_version: 1
    resources:
      - slot: agent
        resource_kind: agent_profile
        resource_id: network-triage-specialist
        tenant_id: "00000000-0000-0000-0000-000000001000"
        workspace_id: "00000000-0000-0000-0000-000000002000"
        version: 1
    config:
      agent_code: network-triage-specialist
      agent_role: "Network Triage Specialist"
      model: "openai-gpt-4o-enterprise"
      task_description: "Analyze incident telemetry, query network topology, and recommend mitigation route."
      max_iterations: 3
      tools: [inspect_topology, query_rag_knowledge, test_circuit]

  # 3. Policy & Guardrail Verification (vRule Matrix)
  - id: policy_decision
    activity_type: ao.activity.governance.policy.check
    contract_version: 1
    resources: []
    config:
      rule_set_id: enterprise_dispatch_matrix
      eval_mode: bytecode_vcel
      fail_action: ESCALATE_HUMAN

  # 4. Human-in-the-Loop Operations Lead Approval Gate
  - id: operations_approval
    activity_type: ao.activity.decision.approval
    contract_version: 1
    resources: []
    config:
      approver_role: operations_lead
      timeout_seconds: 3600

  # 5. Enterprise MCP & Connector Action Execution
  - id: automated_dispatch
    activity_type: ao.activity.connector.http.request
    contract_version: 1
    resources:
      - slot: secret
        resource_kind: vault_secret
        resource_id: secret://vault/telco/bss_api_key
    config:
      method: POST
      url: "{{env.PROVISIONING_GATEWAY}}/api/v1/circuit/dispatch"
      headers:
        x-vastar-service: vastarorch
        x-service-identity: gateway:vastarorch-enterprise
Vastar Architecture Hierarchy
Understanding the Roles of vFlow, VastarOrch, and VastarFusion
The Vastar product architecture is engineered in transparent tiers based on computational demands, delivering extreme cost efficiency without compromising enterprise reliability.
vFlow
Open-spec deterministic workflow runtime (VWFD). Zero-dependency, ultra-low memory footprint (<10MB), and enterprise-grade crash resilience. Serves as the execution foundation for all products in the Vastar ecosystem.
VastarOrch
Complete AI orchestration platform: Visual Studio Canvas, Multi-Agent pipelines, MCP Server gateway, Dynamic Tiering, RAG grounding, and industry connectors. Delivers 100% orchestration functionality with zero shared SaaS risk, running 100% inside your own VPS / Cloud infrastructure via VastarIPShield.
VastarFusion
Ultra-scale real-time digital twin and high-frequency industrial physics simulation platform. Engineered for large-scale energy grid modeling, smart cities, and factory robotics telemetry.
Cross-Industry Mission-Critical Workloads
Proven Enterprise Production Scenarios
From autonomous telco incident triage to central bank regulatory AML trails, explore how VastarOrch executes deterministic workflows across mission-critical industries.
Telco & Network Operators
Autonomous network alert triage, dynamic multi-vendor circuit provisioning, SLA fault recovery orchestration, and high-speed telecommunications billing stream reconciliation.
Key Mission-Critical Use Cases
- Self-healing virtual network routing & automated alert triage
- Automated multi-vendor BSS/OSS service provisioning
- High-volume call detail & rating stream reconciliation
- Agentic customer incident escalation & root-cause analysis
Banking & Fintech
Real-time fraud scoring pipelines, automated AML investigation workflows, micro-settlement orchestration, and immutable regulatory compliance trails ready for central bank & financial authority audits.
Key Mission-Critical Use Cases
- Multi-factor transaction fraud detection & instant decisioning
- Automated Anti-Money Laundering (AML) audit pipelines
- High-throughput micro-settlement workflow durability
- Cryptographically verified compliance run receipts
Logistics, Ports & Customs
Automated cargo manifest verification, cross-border customs document validation, inter-warehouse shipping pipelines, and event-driven fleet container tracking.
Key Mission-Critical Use Cases
- Automated customs declaration & manifest cross-validation
- Multi-carrier shipping route optimization & handoff pipelines
- Port terminal container movement event coordination
- Cold-chain anomaly alerting & human-in-the-loop dispatch
Manufacturing & Industry
Industrial sensor telemetry triage, predictive equipment maintenance dispatch, multi-plant inventory synchronization, and automated visual QA inspection escalation.
Key Mission-Critical Use Cases
- Predictive machine maintenance alerts & autonomous work orders
- Real-time multi-factory inventory balance & replenishment
- Automated visual defect inspection pipeline triage
- SCADA / OPC-UA event ingestion & compliance logs
Mining & Energy
Heavy fleet dispatch coordination, remote site IoT telemetry triage, automated HSE incident reporting, and energy grid load-balancing workflows.
Key Mission-Critical Use Cases
- Remote pit telemetry monitoring & autonomous triage
- Haul truck & heavy fleet schedule optimization
- Automated Health, Safety & Environment (HSE) reporting
- Renewable energy substation load shifting orchestration
Smart City & Public Infrastructure
Municipal citizen report routing, public utility anomaly detection, multi-agency emergency dispatch, and unified sovereign municipal data integration.
Key Mission-Critical Use Cases
- Citizen grievance triage & multi-agency routing
- Water and electrical utility telemetry monitoring
- Emergency service dispatch & coordinate handoff
- Inter-departmental sovereign data pipeline governance
Core Platform Capabilities
Engineered for Complete Enterprise Autonomy
Six foundational engineering pillars delivering deterministic AI orchestration, visual DAG authoring, hardware-rooted security, and zero multi-tenant risks.
Governed Multi-Agent AI Pipelines
Deploy autonomous AI agent squads bound by deterministic VastarOrch contracts (ao.activity.ai.agent.*). Equipped with live testbenches for Human-Facing & M2M Autonomous agent types in Studio with full ReAct reasoning audit trails.
Native Model Context Protocol (MCP)
Bidirectional integration with Cursor and remote IDE agents via RFC 8414/9728 OAuth 2.0. Manage 130+ public and custom connector catalogs directly in the Studio MCP Hub.
Visual Studio Canvas & Declarative YAML
Visual drag-and-drop authoring with 100% real-time bidirectional synchronization with canonical VastarOrch declarative YAML (ao.*). Complete with interactive DAG canvas and in-depth node inspectors.
100% Sovereign Pure BYOC via VastarIPShield
Zero shared SaaS risk. VastarOrch is delivered into your own VPS / Cloud infrastructure protected by VastarIPShield silicon TEE (AMD SEV-SNP / Intel TDX / Nitro Enclaves) with complete data custody.
Zero Trust RBAC & Workspace Isolation
Cryptographic per-workspace canvas isolation, per-tenant boundaries, role-based access control, and tail audit verification ensuring absolute corporate data security.
Co-Located In-Runtime vRule, Transform & Compute
Native co-located Rust runtime running workflow state machines, compiled vRule bytecode (<50µs), native v-cel/Starlark transformation, and Wasm compute together — eliminating external DMN network/gRPC hops and broker latency.
Sovereign BYOC Editions
Everything is Sovereign BYOC: 100% Data Custody via VastarIPShield
Eliminating shared multi-tenant SaaS risks entirely. VastarOrch operates as a pure BYOC software platform delivered into your private VPS or Cloud infrastructure (Onidel, Servury, VPSBG, Akash, Scaleway, AWS, GCP, Azure, Bare-Metal) with VastarIPShield hardware TEE protection, transparent /vCPU licensing starting at $3/vCPU, and strict max_vcpu caps preventing enterprise horizontal exploitation.
Basic BYOC
Ideal for solo developers, lightweight internal tooling, and single-service backends.
- UNLIMITED Workflow Runs
- max_vcpu: 1–2 (Strict Hardware Cap)
- Single Node VPS (Onidel AMD SEV-SNP / Hetzner)
- 15–35 Dedicated DB Connections Pool
Production Enclave
Fullstack production core backend for sustained APIs, CDC WAL, and polyglot AI sidecars.
- UNLIMITED Workflow Runs
- max_vcpu: 2–8 (Hardware Enclave Cap)
- 64MB Shared Memory (SHM) Zero-Copy Bus
- 50–350 Dedicated DB Connections Pool
Enterprise Quorum
Mission-critical financial infrastructure, multi-AZ active-active quorum, and Byzantine Raft cluster mesh.
- UNLIMITED Workflow Runs
- max_vcpu: 12–128+ Fleet Fabric
- Customer BYOK (AWS KMS / HSM / Azure Key Vault)
- 400–5,000+ Dedicated Connections Pool
Strict Hard Cap (max_vcpu Anti-Exploit Enforcement)
To prevent enterprise organizations from evading higher-tier licensing by horizontally chaining basic low-tier nodes, each tier enforces a strict hardware ceiling (max_vcpu). The VastarIPShield Enclave Daemon directly inspects hardware CPU topology (/proc/cpuinfo & cryptographic attestation receipt). Any node or cluster exceeding its tier cap will be blocked from decrypting the container image until an upgrade is completed.
Detailed BYOC Edition Comparison
| Feature Dimension | Basic BYOC | Production Enclave | Enterprise Quorum |
|---|---|---|---|
| Architectural Role & Positioning | Micro-enclave vFlow engine for solo devs, startups & lightweight internal automation (<10MB RAM footprint). | Fullstack production core backend for sustained APIs, background queues, CDC WAL, and polyglot AI sidecars. | Mission-critical financial infrastructure, multi-AZ active-active quorum, and Byzantine Raft cluster mesh. |
| Compute Model & Hosting | 100% Customer Private VPS (Onidel AMD SEV-SNP / Hetzner). Ultra-lightweight 1–2 vCPU footprint. | 100% Customer Cloud / VPS (Hetzner Dedicated, AWS, GCP, Azure CVM). 2–8 vCPU sustained compute. | 100% Customer Clustered Enclave Fleet (Multi-Node AWS, GCP, Azure, Bare-Metal). 12–128+ vCPU fabric. |
| Database Connection Pooling | 15 – 35 dedicated connections pool directly to customer Postgres / MySQL / SQLite. | 50 – 350 dedicated connections pool to Postgres/MySQL/ClickHouse (Zero pool starvation). | 400 – 5,000+ dedicated connections pool across clustered nodes without public internet exposure. |
| Strict Hard Cap (max_vcpu Anti-Exploit) | Max 1–2 vCPU (Single Node Only). Horizontal cluster scaling disallowed on basic tiers. | Max 2–8 vCPU per node/cluster. Cryptographically verified by VastarIPShield enclave daemon. | Max 12–128+ vCPU fleet aggregate. Enforced by hardware TEE CPU topology attestation receipts. |
| Execution Runs & Pricing Model | UNLIMITED Runs • Combined Software starts from $5.00/mo ($5/vCPU) • Est. Real TCO ~$9.50/mo on Onidel VPS! | UNLIMITED Runs • Combined Software starts from $20.00/mo ($10/vCPU, range $20–$144/mo) • Zero per-task tax penalties. | UNLIMITED Runs • Combined Software starts from $240.00/mo ($20/vCPU, range $240–$2,816/mo) • Multi-node Byzantine quorum. |
| Code Isolation & Polyglot Sidecars | Native vFlow deterministic state machine (<50µs execution) with ultra-low memory footprint. | 64MB Shared Memory (SHM) zero-copy bus (<10µs IPC) + isolated MicroVM (Python, Go, Node.js, Rust). | Multi-Node Hardware TEE Memory Isolation + High-Density 64MB SHM Sidecars inside customer secure perimeter. |
| Key Sovereignty & Secret Vault (KMS) | Zero Vendor Access. Secrets and API keys remain 100% inside customer encrypted local VPS vault. | Dedicated Vault KMS Envelope Encryption per instance (Zero secret plaintext leakage). | Customer BYOK (Bring Your Own Key) via AWS KMS / Azure Key Vault / Hardware HSM (Vastar has zero access). |
| Procurement & Activation Channel | Instant Online Checkout (QRIS, Google Pay, Apple Pay, 6 Bank VAs, Cards) via pricing.orch.vastar.id | Instant Online Checkout or Cloud Marketplace with multi-currency dynamic billing (USD / IDR). | Enterprise Sovereign Agreement, Custom Invoicing, or Cloud Marketplace Private Offer. |
| Regulatory Compliance & Standards | Data isolation in customer VPS, GDPR and UU PDP compliant by architecture. | Enterprise audit ready, ISO 27001 ready, SOC 2 Type II, end-to-end encryption in-transit & at-rest. | OJK, Central Bank / BI, HIPAA, GDPR, ISO 27001, SOC 2 Type II (Absolute national data sovereignty). |
Target Infrastructure Catalog
Deploy on Confidential VPS, Sovereign Clouds, or Bare Metal
Onidel Confidential VPS
AMD SEV-SNP hardware attestation with ultra-low TCO (~$4.50/mo server). Perfect for Basic BYOC.
Servury Confidential Cloud
High-density European confidential compute with hardware-rooted memory encryption.
VPSBG Dedicated Enclaves
Independent privacy-first Bulgarian hosting with custom hardware CPU security profiles.
Hetzner Dedicated & Cloud
Cost-effective bare metal & VPS compute across EU & US data centers.
Scaleway Sovereign Bare Metal
European sovereign cloud with 100% GDPR and French/EU regulatory compliance.
Akash DePIN Sovereign Mesh
Decentralized physical infrastructure network for permissionless, censorship-resistant compute.
AWS (EC2 Nitro Enclaves)
AWS Nitro Enclaves, AMD SEV-SNP EC2 instances, and VPC Peering.
Google Cloud Platform (CVM)
GCP Confidential VM with AMD SEV-SNP and Cloud KMS integration.
Microsoft Azure (Confidential)
Azure Confidential VMs (Intel TDX / AMD SEV-SNP) and Azure Key Vault HSM.
Platform Architectural Matrix
VastarOrch vs Leading Backend & Workflow Platforms
Direct architectural breakdown across 24 mission-critical categories: clustered enterprise scheduler, native v-cel & Starlark transformation, sandboxed Wasm/Starlark compute, co-located vRule engine, polyglot SHM sidecars, industrial Tri-Lane ingress (OPC-UA/Kafka/NATS), workflows, dedicated DB pooling, sub-ms Dual-Mode latency, signed Ed25519 provenance, and predictable flat server pricing.
Save $10k–$50k/yr on recipe task tax. High-throughput Tri-Lane ingress (OPC-UA/Kafka/NATS) + sub-millisecond dual-mode (<1ms) + dedicated DB pool (25–800 conn).
Visual canvas + code authoring with deterministic vRules. Built-in Clustered Enterprise Scheduler with civil calendar fold policy + zero worker boilerplate.
Co-located vRule engine (<50µs) running inside the exact same Rust runtime — eliminating Zeebe decoupled DMN gRPC serialization latency (up to 97× throughput).
Fullstack core backend engine (DB pools, HTTP APIs, background queues) with deterministic guardrails and version digest pinning.
100% dedicated hardware with zero multi-tenancy throttling, built-in Clustered Enterprise Scheduler, dedicated DB pool, and UNLIMITED runs.
| Capability Dimension | 🛡️ VastarOrch (Pure BYOC) | Workato (iPaaS) | Temporal | Camunda 8 | LangGraph | n8n |
|---|---|---|---|---|---|---|
|
Visual + Code Workflow Authoring (Polyglot Sidecars)
Visual DAG canvas combined with isolated polyglot code execution (Python, Go, JS, Rust) |
✓✓ Visual + Polyglot Visual DAG Canvas + Isolated Polyglot Sidecars (Python, Go, JS, Rust) |
✓ Recipe Builder Visual recipe builder + custom connector SDK |
Code Only Code-first SDK only (Go, TypeScript, Java, Python, .NET) |
✓ BPMN Modeler BPMN 2.0 visual modeler + external workers |
Code Only Code-only Python / TypeScript state graph definitions |
✓ Node Editor Visual node-based graph editor + JavaScript code nodes |
|
Crash-Proof Durable Execution & WAL Saga (Auto-Resume)
Distributed state machine resilience, zero state loss on restart, automated saga recovery |
✓✓ Durable WAL Dual-Mode: Ephemeral (<1ms) + Durable Saga WAL auto-resume |
✓ Persistent Jobs Persistent recipe jobs dengan auto-retry dan step replay |
✓✓ Event Replay Replay-based deterministic event-sourced execution engine |
✓✓ Zeebe Stream Zeebe distributed stream-processing state engine |
✓ Checkpoint State State checkpointing & human-in-the-loop pause/resume |
◐ Redis Queue Redis execution queue & basic error-trigger retry |
|
Dual-Mode Ingress & Sub-Millisecond Latency
Synchronous real-time API gateway (<1ms) vs long-running background orchestration |
✓✓ Native Dual-Mode Ephemeral Fastpath sub-milidetik (<1ms) untuk API inti + Durable WAL |
◐ Cloud Broker Cloud webhook latency 200ms–1500ms or 5-min polling; cannot serve <1ms synchronous APIs |
◐ Async Queue Start/Signal requires 15ms–50ms+ persistence latency; unsuitable for <1ms synchronous APIs |
◐ Zeebe gRPC Zeebe Raft cluster commit latency ~20ms–100ms before returning a response |
◐ REST Gateway LangGraph Cloud REST latency ~100ms–500ms with tracing overhead |
◐ Event Loop Webhook response ~50ms–250ms (slower during high Redis queue backlog) |
|
Automated Saga Compensation & Rollbacks
Declarative compensating transaction flow to undo distributed state on step failure |
✓✓ Native Saga Graph Native declarative compensation_step & bidirectional rollback graph |
◐ Manual Recipes Manual error handling blocks and custom compensation recipes built by hand |
✓✓ Code-Defined Compensations defined in activity code (Go/TypeScript try-catch sagas) |
✓✓ BPMN Comp. BPMN 2.0 Compensation Intermediate Events & Boundary Events |
✓ Custom Edges Conditional error rollback branches via custom graph edge logic |
— Not Supported Manual Error Workflow trigger without rollback awareness or compensation state |
|
Built-in Scenario Testing & Deterministic Mocking
Native test suite in Studio & Runtime: replay scenarios, deterministic mocks, assertion trees, and zero side-effect execution |
✓✓ Studio & CLI Testbench Native scenario runner, mock trees for DB/APIs/AI, regression assertions, and zero-side-effect test execution |
◐ Live Test Mode Test recipe runs against live connected systems; no native deterministic mock generator or fixtures |
✓✓ Test Framework Time-skipping test environments in Go/TS/Java SDKs with comprehensive activity mocking |
◐ Zeebe Process Test zeebe-process-test Java library for unit testing BPMN workflows in CI/CD |
◐ LangSmith Eval LangSmith evaluations and datasets for offline testing; requires custom mock adapters |
◐ Manual Pin Data Pin Data feature saves previous node execution data; lacks automated assertion trees and regression suites |
|
Clustered Enterprise Scheduler & Calendar Engine (vFlow Scheduler)
Crash-proof distributed scheduler with PostgreSQL lease authority, Native Admission Bridge outbox, civil time/DST fold policies, bounded misfire recovery, multi-tenant fairness, and native lifecycle reconciliation |
✓✓ Clustered Scheduler PostgreSQL firing authority, Native Admission Bridge outbox, immutable runtime pins, DST fold policy, bounded catch-up, multi-tenant budget backpressure, & clock skew incident fencing |
◐ Polling / Interval Interval-based polling triggers (5-minute standard minimum); not designed for sub-second precision, calendar fold policies, or bounded misfire recovery |
✓ Code Schedules SDK-defined workflow schedules (ScheduleHandle) recorded in history; robust but requires manual code authoring without standalone visual calendar outbox |
✓ BPMN Timer Stream BPMN 2.0 Timer Events executed via Zeebe Raft stream; tightly bound to process definitions without dedicated multi-tenant budget backpressure |
— External Cron No built-in scheduler; relies on external cron triggers (AWS EventBridge, Cloudflare Triggers, or host crontab) |
◐ Node-Cron Memory Schedule Trigger node running node-cron on Node.js event loop / basic Redis queue; vulnerable to lost ticks during container restarts |
|
Native Activity: In-Runtime Transformation Engine (v-cel & Starlark)
Sub-microsecond deterministic in-memory transformation, schema projection, and proto shaping via compiled v-cel (2–47ns) and Starlark vs slow script/FaaS steps |
✓✓ In-Runtime v-cel & Starlark Built-in v-cel (<50ns hot-path) & v-starlark transformation engines co-located in runtime • Zero network serialization • Native Protobuf/JSON access |
◐ Formula Mode Basic cloud-evaluated Ruby subset formulas; rate-limited and lacks native binary Protobuf transformations |
— Worker Host Code No built-in transformation node; must be written manually within external activity worker code |
◐ FEEL Expressions FEEL expression evaluation; basic projections work, but complex transformations require external worker routing |
◐ Python Dict Mapping Dictionary comprehension & Pydantic transforms in Python host process |
◐ JS Code / JMESPath JavaScript code nodes in Node.js VM or JMESPath nodes with high memory footprint and slow parsing |
|
Native Activity: In-Runtime Sandboxed Compute (Starlark & Wasm)
Safe, deterministic, in-process algorithmic compute via precompiled Starlark (~162ns floor) and WebAssembly (Wasm) without heavy container overhead |
✓✓ Starlark & Wasm VM In-runtime deterministic compute via cached v-starlark (~162ns floor) & native Wasm sandboxes • Zero cold start • Instant memory-safe execution |
— Proprietary Cloud Proprietary cloud step execution; cannot run arbitrary Wasm binaries or custom algorithmic models locally |
— External Workers Compute runs on user-managed external worker fleets; no sandboxed compute engine inside Temporal Server |
— External Job Workers Zeebe delegates compute to external job worker applications over gRPC network streams |
◐ Host Python VM Runs inside host Python interpreter; lacks isolated sandboxed Wasm bytecode runtime |
◐ Node.js Subprocess Runs in Node.js process with vm2 sandbox or external task runners; vulnerable to memory leaks |
|
Co-Located Business Rule Engine in Same Runtime (vRule vs Decoupled DMN)
Compiled bytecode rules (<50µs) co-located in the same native workflow runtime without IPC/network hops vs decoupled/external DMN engines |
✓✓ In-Runtime vRule (<50µs) Compiled bytecode vRule engine co-located in same native workflow runtime (<50µs) • Zero IPC/network hop • Schema-bound facts & decision tables with hit policies |
◐ Lookup Tables Basic lookup tables & formula field expressions (Ruby subset) |
— Host Code None; business rules must be manually written in application code |
◐ Decoupled DMN (gRPC Latency) DMN 1.3 decision tables & FEEL expressions, but executed across decoupled Zeebe worker/broker gRPC boundaries with serialization latency |
— Code Routing None; conditional logic hardcoded within Python routing functions |
◐ Switch / If Node Basic If/Switch nodes with JavaScript regex expressions |
|
Governed AI Agents as Versioned Resources (Model + Tools + Rules)
Agent + Model + Tools + Rules + Authority bound as immutable pinned version/digest |
✓✓ Governed Registry Agent Profile lengkap (Prompt, Tools, Rules, Ingress/Egress Guardrails) terikat hash permanen |
✓ Agent Studio Workato Agent Studio + enterprise connectors & guardrails |
◐ Code Wrapped AI Agents implemented manually as Temporal Activities (LLM wrappers) |
◐ AI Connectors Isolated AI connector tasks (OpenAI/HuggingFace) within BPMN tasks |
✓✓ Agent Graphs Stateful multi-agent graphs with LangSmith Deployment |
✓ AI Agent Node Basic AI Agent nodes + LangChain tools (OpenAI) |
|
Native Model Context Protocol (MCP) Tooling
First-class support for MCP tools, agents, and sandboxed client/server execution |
✓✓ Native Protocol MCP client/server native dengan zero-knowledge secret vault injection |
✓ MCP Connectors Workato Agentic MCP connectors for enterprise systems |
◐ Community Self-implemented via community activities (no native runtime gateway) |
◐ Custom Connectors Custom REST/gRPC connectors wrapping MCP tools |
✓ LangChain MCP LangChain MCP client adapters & tool calling protocols |
✓ Community Nodes Built-in MCP Client node to connect with local MCP servers |
|
Unified Governed Resource Registry
Single pane of glass managing Models, Agents, Rules, Connectors, KB, Sandboxes |
✓✓ Unified Plane Registri kanonik terpusat untuk Model, Agent, Rule, Konektor, KB, Compute & Sandbox |
✓ App Connections Unified App Connections, Recipes, Community Connectors, and Data Tables |
— Application Libs No central registry; defined within customer application codebases |
◐ Zeebe Registry Zeebe deployment registry for BPMN & DMN process definitions |
◐ Prompt Hub LangSmith prompt & agent hub (monitoring and prompt registry) |
◐ Community Store Community node repository and local encrypted credentials |
|
Native Backend Primitives (DB, Queues, Micro-Engine)
Built-in primitives: HTTP, DB pool, queues, object storage, detached tasks, cron |
✓✓ Full Backend Primitives Database pool terdedikasi, HTTP gateway, queues, cron, detached tasks, blob storage |
✓ Enterprise Bus Enterprise connectors, webhook listeners, pub/sub topics, and data tables |
Code (SDK) Distributed timers, signals, queries, updates, and child workflows in code |
✓ BPMN Primitives Service tasks, message events, timers, user tasks, and out-of-the-box connectors |
◐ Checkpoint Memory State memory checkpointers, queues, stores, and human-in-the-loop interrupts |
✓ Node Integrations HTTP Request, Webhook, Schedule, Wait nodes, and hundreds of integration modules |
|
Dedicated Database Connection Pooling (Zero Pool Starvation)
Dedicated persistent connection pools (25 to 800 conn) directly attached to customer DB |
✓✓ 25–800 Conn Pool Pool koneksi DB dedicated terisolasi (25–800 koneksi) per tenant via VPC Peering |
◐ OPA Agent Tunnel On-Prem Agent (OPA) WebSocket tunnel with shared connection limits |
— External DB Cluster database managed separately from workflow execution workers |
— Zeebe Engine Zeebe engine writes to disk/OpenSearch; does not manage customer DB connection pools |
— External Store Ephemeral Postgres connection per checkpointer without dedicated pooling |
◐ Single DB Node DB nodes open connections per run, vulnerable to pool starvation during traffic spikes |
|
Sidecar Activity Node: Polyglot Sidecar via IPC Shared Memory (64MB SHM Bus)
Out-of-process polyglot sidecars (Python, Go, Node.js, Rust) alongside engine runtime connected via 64MB zero-copy Shared Memory bus (vil_shm, <10µs IPC) |
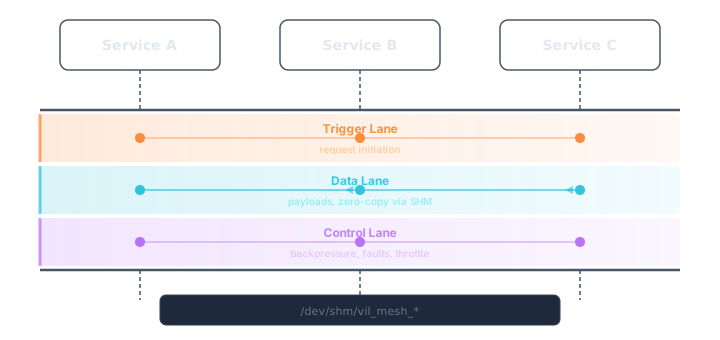
✓✓ 64MB SHM IPC (<10µs) Polyglot sidecar activity nodes alongside runtime via zero-copy 64MB Shared Memory bus (vil_shm, <10µs IPC) for high-performance Python/Go/Rust |
— Not Supported No local sidecar processes; connectors communicate via external cloud APIs |
◐ Activity Network Activities communicate with workers via gRPC network calls across workers |
◐ Zeebe gRPC External job workers poll Zeebe engine over gRPC network connections |
◐ In-Memory Python Fast in-process execution inside same Python interpreter; cross-language requires HTTP |
— Subprocess / TCP Code node runs within Node.js vm2 or subprocess; no multi-language shared memory bus |
|
Tri-Lane Protocol & High-Throughput Industrial Ingress (OPC-UA, Kafka, NATS, MQTT)
Physical separation of Trigger, Data, and Control lanes eliminating Head-of-Line blocking, native industrial connectors (OPC-UA, Modbus, NATS KV, Kafka, TiKV) with 895k rec/s zero-copy throughput |
✓✓ Tri-Lane Zero-Copy Tri-Lane architecture (Trigger/Data/Control), zero-copy ExchangeHeap, native industrial connectors (OPC-UA, Modbus, MQTT, NATS JetStream, Kafka, TiKV) |
◐ Cloud iPaaS Extensive cloud enterprise connectors, but high cloud latency (200ms–1500ms) without zero-copy streaming for local SCADA/factory telemetry |
◐ gRPC Workers Workflow ingress exclusively via gRPC client SDKs; Kafka/MQTT/OPC-UA ingestion requires custom developer-built workers outside engine |
◐ Zeebe Ingress Ingress via Zeebe gRPC gateway or outbound connectors; high JSON serialization overhead for real-time sensor streaming throughput |
— HTTP / Python Standard Python REST/WebSocket API endpoints; not designed for high-throughput zero-copy binary stream ingestion |
◐ Community Nodes Community JavaScript MQTT/Kafka nodes; suffers severe throughput bottlenecks on single-threaded V8 under heavy message streaming |
|
Isolated MicroVM & Untrusted Code Sandboxes
Hardware/kernel-level isolation (Firecracker MicroVM / LXC / seccomp) preventing unauthorized host access from untrusted scripts and user code |
✓✓ MicroVM / LXC Hardware-grade MicroVM / LXC sandbox with isolated memory, CPU limits, and seccomp filters |
◐ Cloud Multi-Tenant Custom Ruby/Python code steps execute in Workato managed cloud worker pool |
Code (Self-Hosted) Sandbox and host security must be implemented manually by customer in worker code |
◐ External Worker Executed outside Zeebe cluster; security isolation relies on customer worker environment |
◐ Container Pod LangGraph Cloud runs in container pods; custom sandboxing requires custom infrastructure |
◐ Node vm2 / Worker JavaScript vm2 sandbox or external task runners; historically prone to VM escape CVEs |
|
Confidential BYOC & Hardware Enclave (Zero Vendor Access)
100% execution in customer VPC with silicon/CPU cryptographic memory isolation (AWS Nitro Enclaves) and customer-owned KMS keys (BYOK) |
✓✓ Nitro Enclaves & BYOK Silicon-level memory encryption (AWS Nitro Enclave), Zero Vendor Data Access, and customer-owned AWS KMS keys |
— SaaS + OPA Agent Central SaaS control plane parses and routes recipe data; On-Prem Agent opens tunnel to Workato Cloud |
◐ Self-Hosted Cluster Self-hostable in private VPC; customer responsible for enclave architecture and KMS integration |
◐ Self-Managed K8s Deployable to private Kubernetes; confidential computing must be handled at the node pool level |
— Cloud SaaS / K8s LangSmith Cloud hosts telemetry and traces; self-hosted enterprise requires full Kubernetes cluster |
◐ Self-Host Docker Self-hostable on customer VM; no native cryptographic enclave attestation or KMS envelope sealing |
|
Multi-Cloud & Edge Compute Portability
Run workflows at the edge, private cloud, AWS, GCP, Fly.io, or on-premise hardware |
✓✓ Any Cloud / Edge AWS EC2/Nitro, Cloudflare Workers Edge, Bare-Metal Proxmox LXC, Fly.io, GCP |
◐ SaaS + On-Prem Multi-tenant Workato Cloud SaaS + On-Premise Agent for local network data |
✓✓ Any Platform Temporal Cloud (AWS) or self-hosted on any server/cloud (Docker/K8s) |
✓ Multi-Cloud Camunda SaaS (AWS/GCP) or self-managed Kubernetes cluster |
✓ Cloud / K8s LangGraph Cloud (AWS) or standalone API deployment on Kubernetes |
✓ Self-Host Docker n8n Cloud (Hetzner/AWS) or self-hosted Docker on any private VPS |
|
Zero-Leakage Secret Vault & Egress Guardrails
Zero-knowledge secret injection, KMS envelope encryption, strict egress data filtering |
✓✓ Zero-Leakage Hashing Vault API Key + pemfilteran egress deterministik + anti prompt-leakage |
✓ Encrypted Vault Enterprise encrypted credential vault with role-based secret masking |
Code-Defined Secrets managed directly within customer worker application code (self-managed KMS) |
✓ Cluster Secrets Zeebe cluster secret management and encrypted environment variables |
✓ Cloud Secrets Secret environment variables managed via LangSmith Cloud or Kubernetes secrets |
✓ Local AES-256 AES-256 encrypted credential storage in local SQLite or PostgreSQL database |
|
Human Approval & Governance Escalation Gates
Native human-in-the-loop approval activities with configurable timeout and audit trails |
✓✓ Native Approval ao.activity.decision.approval terintegrasi dengan timeout, role, & audit trail |
✓ Workbot Approvals Workato Workbot for Slack/Teams interactive approval workflows |
Code (Signals) Durable external signal pattern waiting for human approval within workflow code |
✓✓ User Tasks Native BPMN User Tasks integrated with Camunda Tasklist application |
✓ Interrupt Logic Native interrupt() mechanism in state graphs for human-in-the-loop approvals |
◐ Wait Webhook Wait node with webhook callback URL for basic manual approval gates |
|
Cryptographic Version Digest Pinning (Zero Drift)
Immutable cryptographic digest pinning (SHA-256) across workflows, rules, and agents |
✓✓ Immutable SHA-256 Permanent SHA-256 cryptographic digest locks across workflows, vRules, AI prompts, and sidecars |
✓ Version History Recipe version history with phased release lifecycle (Dev/Test/Prod environments) |
✓ Code Versioning Workflow versioning via explicit code patch API (workflow.getVersion) |
✓ Semantic Version Process definition keys with incremental semantic versioning |
Code (Git) Git commit deployment revisions in LangSmith Platform |
◐ Basic History Basic workflow version history (no cryptographic digest locks) |
|
Signed Terminal Provenance (Ed25519) & Journal Governance
Cryptographically signed execution receipts (Ed25519 canonical envelope v1.3) with multi-storage journal governance (PostgreSQL / TiKV / Cloudflare DO) |
✓✓ Signed Ed25519 Provenance Cryptographically signed receipts (AiVRuleDecisionReceiptV1, Ed25519 24-tuple envelope) with KMS attestation & multi-backend journal governance |
◐ Activity Logs Standard recipe execution audit logs & role-based activity trails (no cryptographic signatures) |
✓ Event History Tamper-evident deterministic event history replay log |
◐ Event Streams Elasticsearch/OpenSearch event stream & Optimize audit reports (no cryptographic sealing) |
— Tracing Spans LangSmith tracing spans (application observability, not cryptographically sealed sovereign audit) |
— Execution Logs Standard execution logs in database without cryptographic signatures or tamper-proof receipts |
|
Pricing Model & Total Cost of Ownership (TCO)
Predictable flat server compute cost vs punitive per-execution / per-task fees |
✓✓ Pure BYOC /vCPU 100% Pure Sovereign BYOC via VastarIPShield • Starts at $3/vCPU (Orch) + $2/vCPU (Shield) • vFlow 1-vCPU TCO ~$9.50/mo • UNLIMITED runs • Strict max_vcpu caps |
— Punitive Task Tax Base license $10,000 – $50,000+/yr PLUS metered per-task quota that rapidly inflates with volume |
◐ Actions / Compute Temporal Cloud bills per Million Actions + storage, or complex self-managed DevOps infrastructure costs |
◐ Metered Instances Tiered metered pricing per task execution / process instance volume |
◐ Step & Token Fee Metered fee per node step execution in LangSmith + LLM token overage fees |
◐ Punitive Run Caps Strict execution caps (2.5k–10k runs/mo on Starter/Pro plans) forcing repeated tier upgrades |
VastarOrch Canonical Schema
Deterministic, Governed Workflow Contracts
No black-box magic. The canonical VastarOrch orchestration contract (vastarorch.workflow/v1) seamlessly ties together ingress triggers, AI Agent invocations (ao.activity.ai.agent.*), policy guardrail checks (ao.activity.governance.policy.*), human approval gates, and critical connector executions (ao.activity.connector.*) with complete mathematical determinism on the vFlow core.
- 100% real-time bidirectional synchronization with VastarOrch Studio Visual Canvas
- Zero schema drift via cryptographic SHA256 version digest pinning
- Immutable audit journal signed by Ed25519 terminal provenance keys
Ready to Deploy Sovereign Agentic Infrastructure?
Eliminate SaaS data leaks, vendor lock-in, and unpredictable per-task bills. Run VastarOrch on your own private cloud or VPS with hardware TEE protection.